
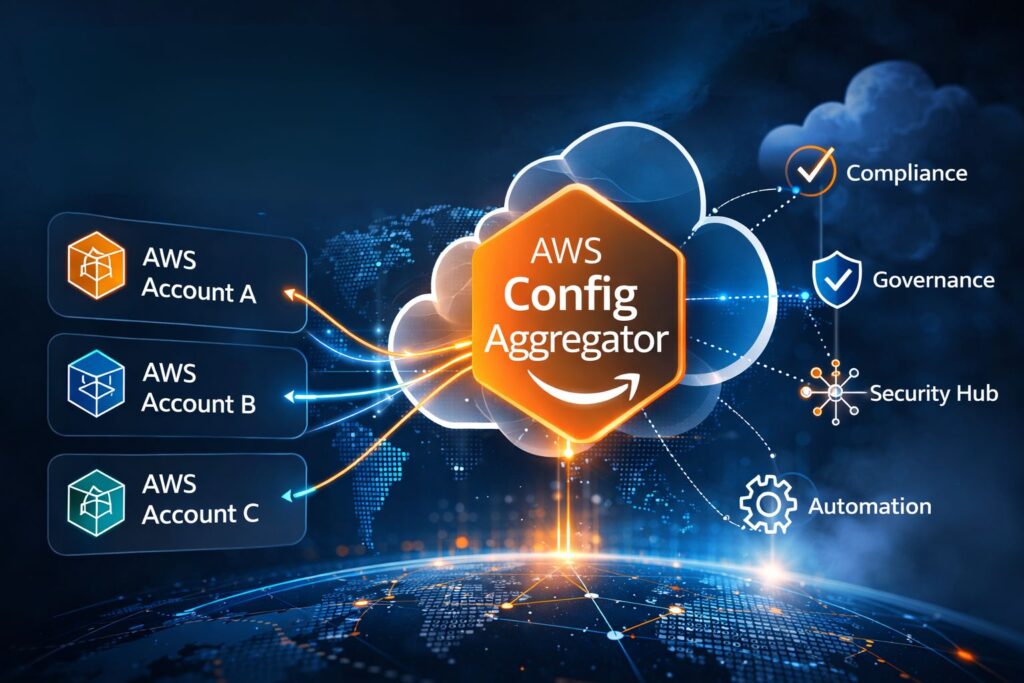
AWS Config Aggregator: Multi-Account Compliance Monitoring in AWS
Introduction The Challenge of Multi-Account Compliance in AWS Organizations leveraging AWS rapidly scale resources and grow into multi-account environments to

Introduction The Challenge of Multi-Account Compliance in AWS Organizations leveraging AWS rapidly scale resources and grow into multi-account environments to

Introduction: VPC Endpoint vs Private Link VPC Endpoint vs Private Link uncovers deeper architectural issues related to public internet exposure

AWS Security Groups vs NACL: Introduction It is a mistake to frame AWS Security Groups vs. NACL as either one
Introduction: Why Architecture is the First Infrastructure Security Control The Hidden Timing of Security Decisions Sun Tzu said that every
Amazon Detective vs GuardDuty for Security Teams: Introduction Security teams handle multiple AWS security services and need to understand their
Difference between AWS Config and Security Hub: The Boundary Problem Because AWS Config and Security Hub are often mentioned together,
Introduction: Custom AWS Config Rules Best Practices The AWS Config service simplifies compliance enforcement for AWS resources in an intuitive,
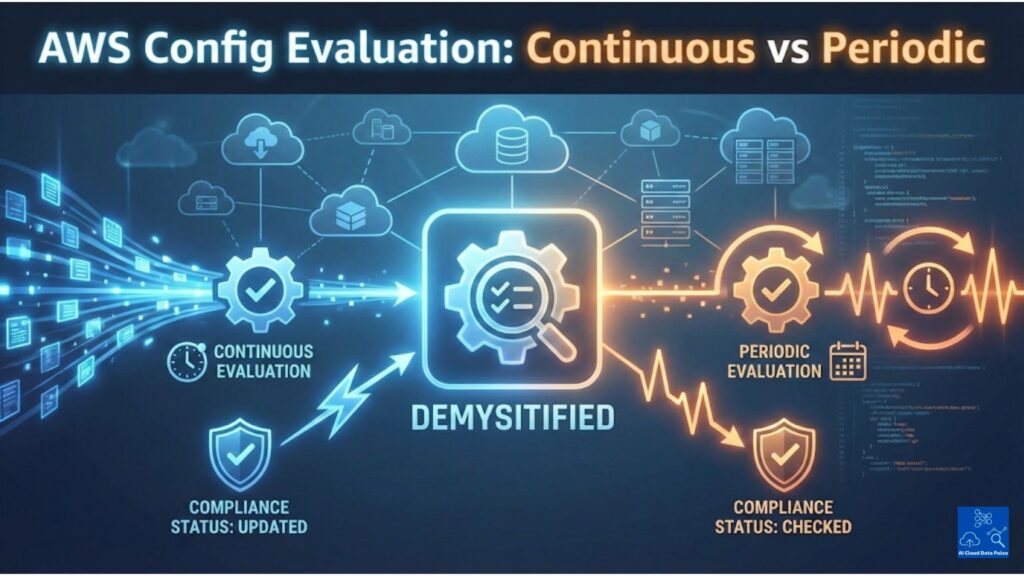
Introduction – Why AWS Config Rule Evaluation Modes Matter AWS Config uses defined compliance rules to evaluate recorded configurations for
Introduction AWS environment compliance is a core requirement for any security posture and is enforced through AWS Config rules monitoring.
AWS Security Hub Findings: Introduction AWS Security Hub findings address the issue of fragmented security signals from multiple independent AWS
