
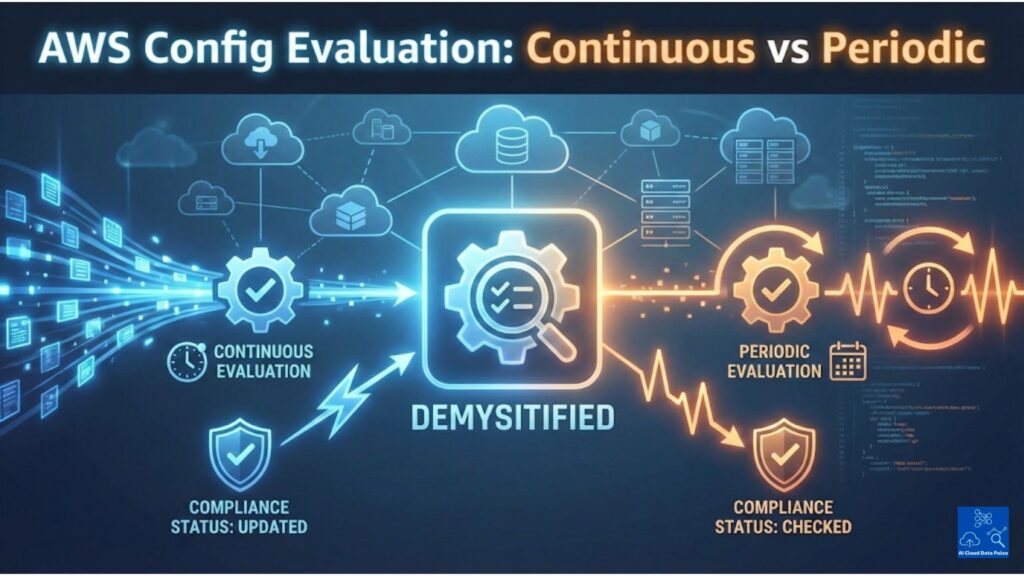
AWS Config Rule Evaluation Modes Demystified
Introduction – Why AWS Config Rule Evaluation Modes Matter AWS Config uses defined compliance rules to evaluate recorded configurations for
Introduction – Why AWS Config Rule Evaluation Modes Matter AWS Config uses defined compliance rules to evaluate recorded configurations for
Introduction AWS environment compliance is a core requirement for any security posture and is enforced through AWS Config rules monitoring.
AWS Security Hub Findings: Introduction AWS Security Hub findings address the issue of fragmented security signals from multiple independent AWS
Introduction To explain VPC Flow Logs, it is helpful to understand the problems they try to solve. AWS services generally
Is AWS GuardDuty a SIEM? Why This Question Keeps Coming Up To better understand whether AWS GuardDuty is a SIEM,
Introduction: GuardDuty Findings Explained Why GuardDuty Findings Are Central to AWS Threat Detection A simple explanation is that GuardDuty findings
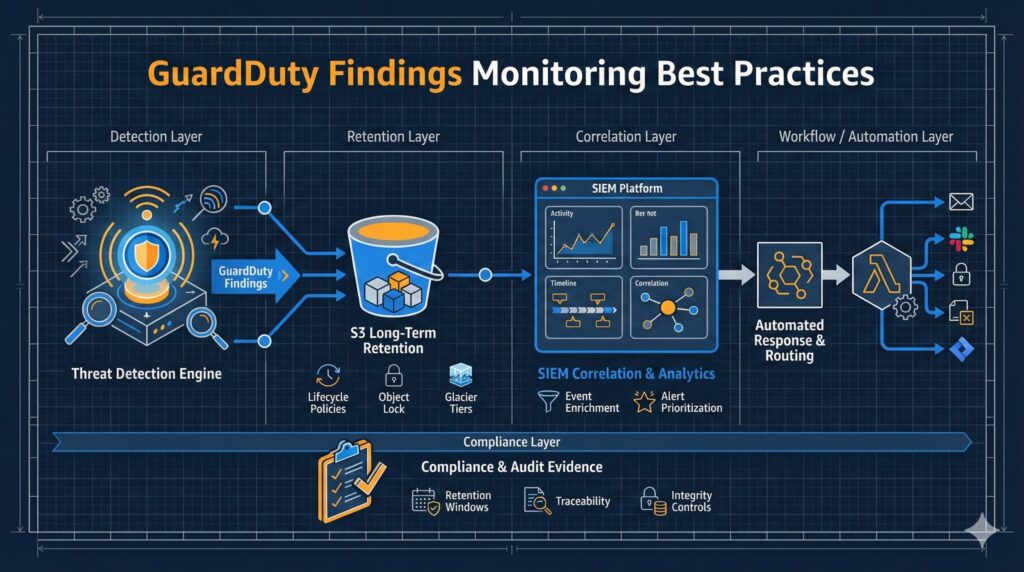
Introduction to GuardDuty Findings: Monitoring Best Practices GuardDuty findings are central to any security response workflow; therefore, best practices around
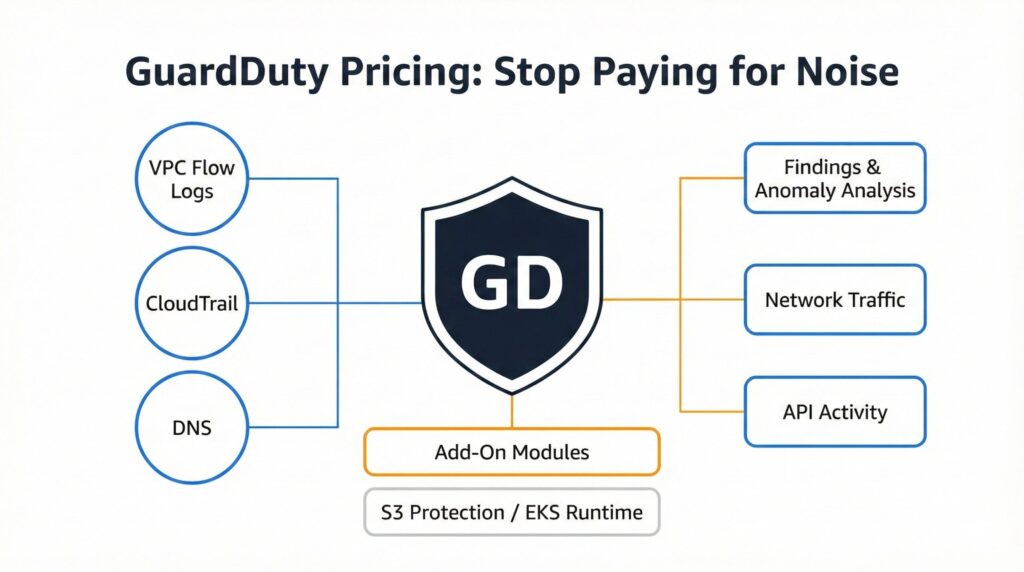
Introduction: Why GuardDuty Pricing Isn’t as Straightforward as It Looks We surveyed GuardDuty best practices, but pricing is of paramount
Best Practices: What Is AWS GuardDuty and Why It Matters AWS GuardDuty Best Practices takes over from AWS Logging and
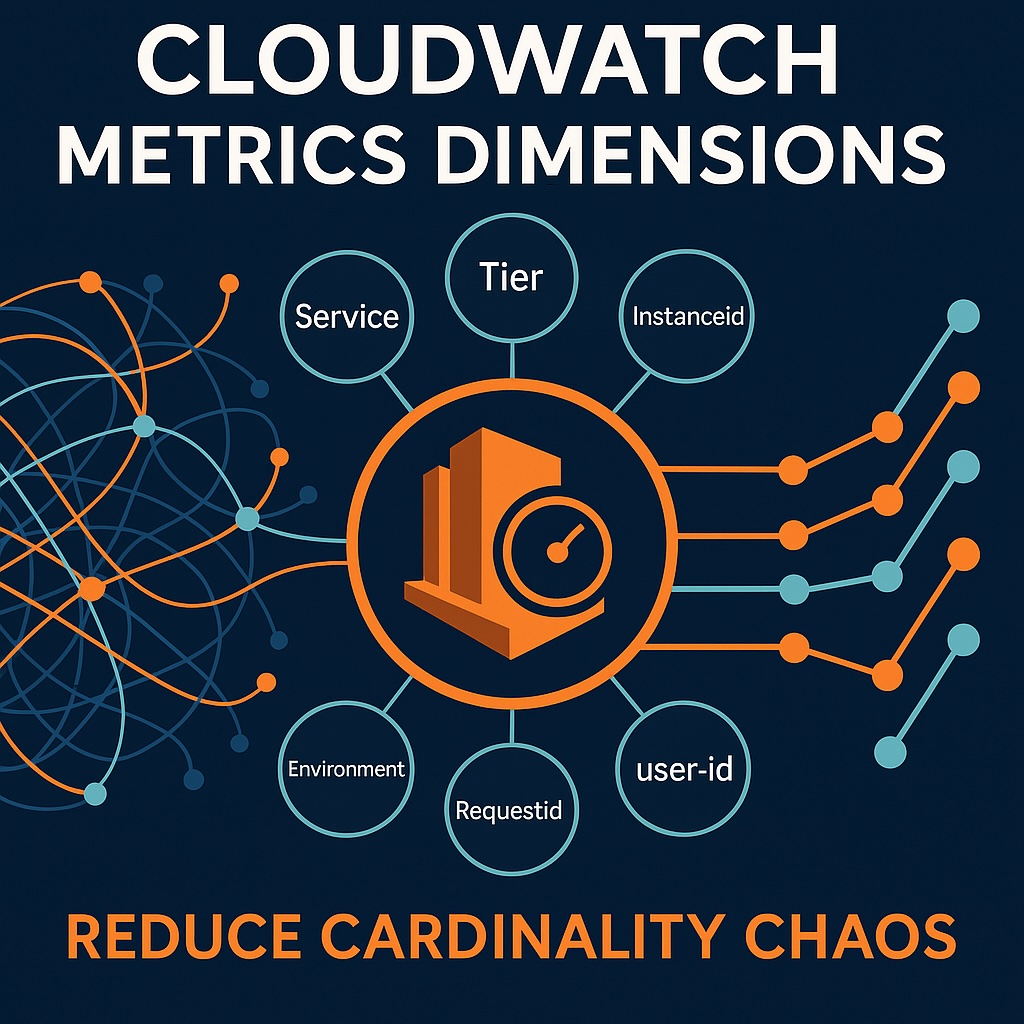
CloudWatch Metrics Dimensions: Introduction to Best Practices Best practices in CloudWatch metrics contribute to a comprehensive view of the cloud
